
The quickest way is the Cloud Manager: tab „SSH“, set „Root Login“ to „SSH Key Only“. This requires the Guest Agent. Manually, you set PasswordAuthentication no in the SSH configuration and restart the SSH service, which works on every Linux server. Important in both cases: first check that logging in with your SSH key works, then turn off the password.
Why it is worth it: every server with an open port 22 gets automated login attempts around the clock. Without password login, these attempts go nowhere, no matter how many there are.
Using the web interface
In the VPS settings of the Cloud Manager you can switch password authentication for the root login on and off. This requires a running Guest Agent. Go to the „SSH“ tab and select „SSH Key Only“ for „Root Login“.
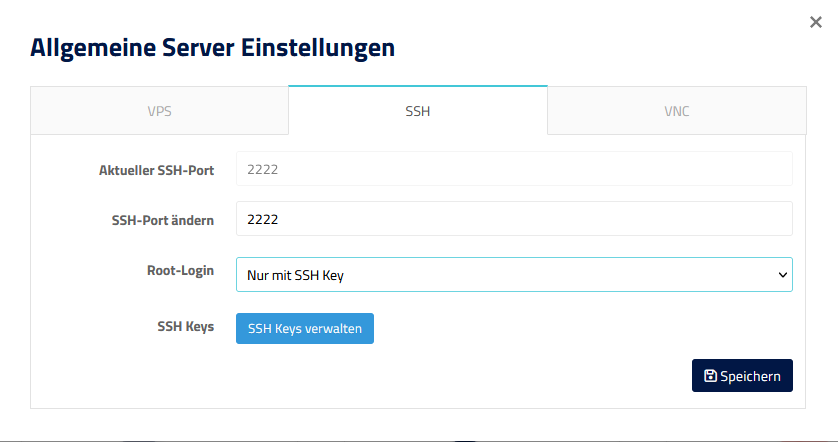
After saving, your server only accepts the root login with an SSH key. If you work with additional users, use the manual way, which applies to all accounts.
Smart Essential: There is no „SSH“ tab here. The web interface only offers the root password reset (also via the Guest Agent). If the Guest Agent is running, you can set the option via the Prepaid-Hoster API. Without the Guest Agent, use the manual way.
Manually via SSH
On Debian and Ubuntu, the SSH service first reads the files in /etc/ssh/sshd_config.d/ and then /etc/ssh/sshd_config. If a setting appears twice, the first value wins. So it is best to create your own file with a low number that is read before all others:
nano /etc/ssh/sshd_config.d/00-ssh-key-only.confContent of the file:
PasswordAuthentication no
KbdInteractiveAuthentication no
PermitRootLogin prohibit-password
PasswordAuthentication noturns off the password login.KbdInteractiveAuthentication nocloses the second way a password can be requested. On Debian this is already the default, the line does no harm.PermitRootLogin prohibit-passwordallows root only with a key.
Save the file and check the configuration for typos. No output means everything is fine:
sshd -tThen restart the SSH service:
systemctl restart sshKeep your current session open. Test in a new window whether you can log in with your key. If that fails, delete the file in the open session and restart the service again.
How to check that it works
The SSH service shows you the values it actually uses:
sshd -T | grep -Ei 'passwordauthentication|kbdinteractive|permitrootlogin'Expected are passwordauthentication no, kbdinteractiveauthentication no and permitrootlogin without-password (the internal name SSH uses for prohibit-password).
From your own computer you can force a password login on purpose. The server has to reject it:
ssh -o PubkeyAuthentication=no root@62.68.75.69The correct answer is Permission denied (publickey). without a password prompt.
Common pitfalls
- The password is still requested: Another file in
/etc/ssh/sshd_config.d/setsPasswordAuthentication yesand is read before yours. A typical one is50-cloud-init.confon Ubuntu.grep -ri passwordauthentication /etc/ssh/finds every occurrence. - A change directly in sshd_config has no effect: Same reason. Values from
sshd_config.dtake precedence because they are read first. - The option in the Cloud Manager is missing or has no effect: The Guest Agent is not running. Install the Guest Agent or use the manual way.
- The key is rejected: Check the permissions.
~/.sshneeds700,~/.ssh/authorized_keysneeds600and must belong to the user you log in with. - PuTTY asks for a password: The private key is not loaded. In PuTTY, set the .ppk file under „Connection“, „SSH“, „Auth“, „Credentials“. Details in Create and use an SSH key.
I have locked myself out
No reason to panic. Via VNC in the Cloud Manager you log in directly at the console. That is not an SSH connection, so the root password still works there. Then delete the new file or fix the setting and restart the SSH service.
Forgot the root password? You can reset it yourself: How do I reset my root or admin password? If the server no longer starts cleanly, the rescue system in the Cloud Manager helps.
 EN:
How do I disable SSH password login?